
In an era dominated by technology, cybersecurity isn’t just a buzzword; it’s a critical necessity. The modern business landscape demands a proactive approach to protecting your data and infrastructure from an ever-evolving threat landscape. 🚀
Why You Need to Take Cybersecurity Seriously
In our latest newsletter, we emphasize the importance of taking cybersecurity seriously and adopting a comprehensive strategy to safeguard your organization. Cyber threats are becoming more sophisticated, and the consequences of a breach can be devastating, both financially and in terms of reputation. Don’t wait until it’s too late; let’s explore the key components of an effective cybersecurity strategy:
🔥 The Benefits of Having a Firewall A robust firewall acts as your organization’s digital gatekeeper, filtering out malicious traffic and ensuring that only legitimate data enters and exits your network. It’s your first line of defense against cyberattacks.
📝 Effective IT Policies Establishing clear and comprehensive IT policies sets the foundation for secure practices within your organization. From password management to data handling, having well-defined IT policies ensures that everyone is on the same page when it comes to security.
🔄 A Resilient Recovery Strategy In the unfortunate event of a cyber incident, a recovery strategy is your safety net. It allows you to bounce back quickly and minimize downtime, protecting your operations and your reputation.
🔐 The Power of a SIEM Solution: Wazuh Security Information and Event Management (SIEM) solutions like Wazuh provide real-time monitoring and threat detection, enabling you to respond swiftly to suspicious activities and breaches. It’s like having a dedicated security team on call 24/7.
💡 We’re here to guide you through the world of cybersecurity, helping you implement these essential elements and stay one step ahead of cyber threats.
Stay tuned for in-depth articles on each of these topics, where we’ll dive into best practices, implementation tips, and real-world examples.
Your security is our priority. Don’t wait; let’s enhance your cybersecurity strategy together.
Act now and let us help you secure your business!
Our Blog
Your Business Continuity Plan: Does Everyone Know Their Role?
A business continuity plan is only as strong as its people Your business continuity plan lists the production manager, sales lead and communications officer. But have those employees ever rehearsed their responsibilities? If not, the document may offer comfort...
Cyberattacks Are Getting Faster. Is Your Business Ready to Respond?
800 TECH | EXECUTIVE CYBER BRIEF 18 NOVEMBER 2026 | 2-MINUTE READ The business issue: Cybercriminals are using artificial intelligence to automate attacks against businesses, reducing the time and effort needed to identify weaknesses, exploit systems and gain...
What Should Leaders Do in the First Hours of a Cyber Incident?
The first hours should activate a cyber incident response plan A finance employee notices unusual messages from a trusted supplier. Soon afterward, colleagues report suspicious sign-in activity. Should the organization disable an account, halt payments or contact...
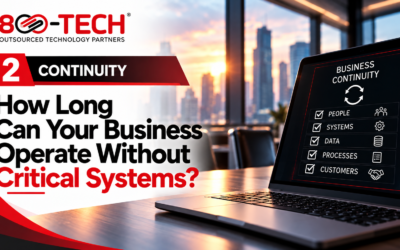
How Long Can Your Business Operate Without Critical Systems?
Which critical systems keep your business operating? Imagine a Caribbean manufacturer whose production scheduling system becomes unavailable during a busy delivery week. Employees may still arrive at work, yet orders, dispatch and customer commitments quickly suffer....
Who Is Accountable for Cybersecurity in Your Business?
Why cybersecurity accountability belongs in the boardroom? A supplier’s compromised account can cause your organization’s problem overnight. When a payment instruction changes or a customer cannot access a service, clients will look to the business, not its IT...
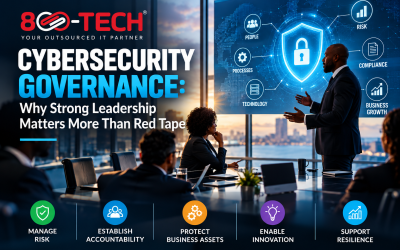
Cybersecurity Governance: Why Strong Leadership Matters More Than Red Tape
When business leaders hear the word governance, they often think of bureaucracy, lengthy approval processes, additional policies and unnecessary restrictions. However, effective cybersecurity governance should achieve the opposite. It should help organizations make...
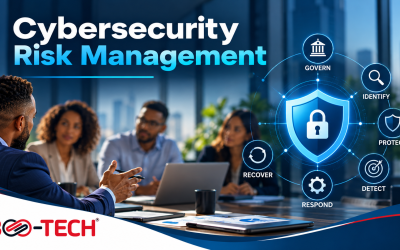
Cybersecurity Risk Management: Don’t Just Pay for Security, Test It!
Many organizations still think about cybersecurity in much the same way they think about insurance: something they pay for in case something goes wrong. It is an understandable comparison, but it creates a dangerous mindset. Cyber insurance can help absorb part of the...
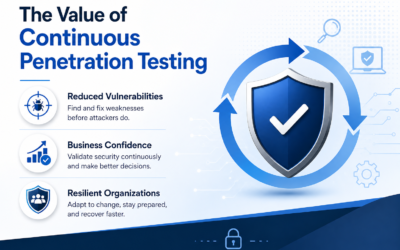
Continuous Penetration Testing: Why Modern Businesses Must Continuously Validate Security
Why Continuous Penetration Testing Matters Business environments never stand still. Every software update, cloud migration, vendor integration, employee onboarding, or configuration change introduces new opportunities for cyber attackers. Therefore, organizations can...
Business Cybersecurity: Why It’s No Longer Just an IT Issue
Business Cybersecurity Is About Business Survival For years, many organizations viewed cybersecurity as the responsibility of the IT department. However, today's business environment tells a different story. Every new employee, cloud application, software update, AI...