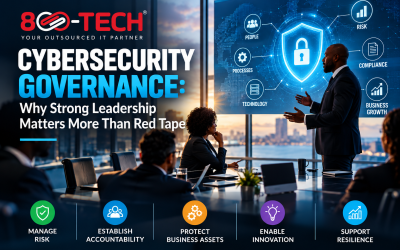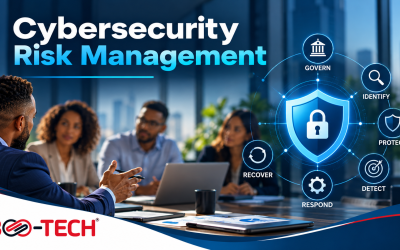
Why cybersecurity accountability belongs in the boardroom?
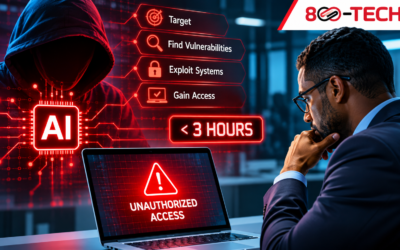
A supplier’s compromised account can cause your organization’s problem overnight. When a payment instruction changes or a customer cannot access a service, clients will look to the business, not its IT contractor, for answers. That is why cybersecurity accountability belongs in leadership discussions before an incident occurs.
During 800 TECH’s Before the Breach webinar, Managing Director Scofield Thomas made a clear distinction: organizations can outsource technical services, but leaders retain accountability for the consequences. Therefore, appointing a provider does not remove the board’s duty to understand exposure, approve priorities, and demand results.
Translate technical risk into business consequences
Executives do not need to configure firewalls. However, they should understand which customer records, payment processes, production systems, and communications channels need protection. Ask what happens to revenue, service delivery, and reputation when one of those assets becomes unavailable.
Marcela Coronell reinforced the need to connect security decisions to business priorities. For example, a Trinidad and Tobago distributor may depend on email approvals, inventory records and supplier transactions. A compromise that delays orders is not merely a technical issue; it is a commercial interruption.
Demand evidence rather than reassurance
A statement that the company has antivirus software or a security provider is not enough. Instead, leadership should request understandable risk reports, findings from assessments, evidence of corrective action, and a clear account of unresolved weaknesses.
Scofield compared this oversight with reviewing financial statements. Just as a CFO explains unexpected expenditure, a technology or security lead should explain material exposure. Additionally, independent validation can uncover blind spots that routine operations miss. Junior Gilpin stressed that organizations cannot improve risks they have never measured.
Three actions executives can take this quarter
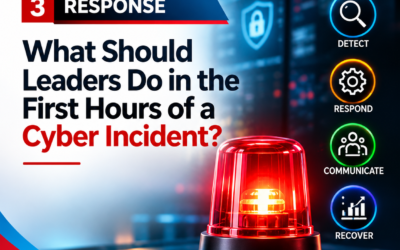
First, designate an executive owner who can escalate material cyber risks to the board. Second, request a concise report covering critical assets, leading risks, outstanding actions, and deadlines. Third, schedule a recurring review where business owners decide whether to mitigate, transfer, or formally accept each significant risk.
These steps make cybersecurity accountability measurable. Moreover, they give the IT team a clear decision-making route rather than leaving important trade-offs unresolved.
FAQ: Can cybersecurity accountability be outsourced?
No. A managed service provider can operate controls, investigate alerts and advise on remediation, but company leaders still decide risk appetite, funding and business priorities. Consequently, contracts should define service responsibilities without confusing them with executive accountability.
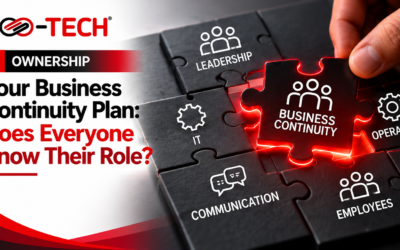
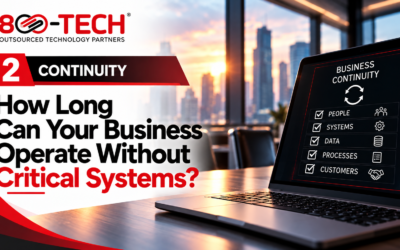
Explore the related discussion on business continuity roles and training and review the webinar resource hub for the five leadership questions.
What a useful executive cyber risk report should show
A useful report should start with the business services at risk, not a long list of technical alerts. It should identify the system or process involved, the likely business consequence, the person responsible, and the date by which management expects a decision or remedy. Leaders should also see what has changed since the previous review.
For example, an unresolved weakness in supplier email verification matters because fraudulent payment instruction could divert funds. The report should explain whether employees have a reliable callback process, whether the organization has tested it, and who will close any gaps. In this way, a board can distinguish a documented control from a working one.
How to make governance routine rather than reactive
Cybersecurity accountability becomes more practical when executives include it in normal business reviews. Finance already reports on cash flow and budget variances. Similarly, operations report on delivery performance. Security reporting can follow the same discipline: a short dashboard, material exceptions, decisions required, and progress against commitments.
However, management should avoid turning this into a blame exercise. Teams need a safe route to report concerns early. An executive sponsor can remove obstacles, approve proportionate improvements, and ensure that security decisions reflect the organization’s priorities. This approach also helps smaller Caribbean businesses that lack a dedicated security department.
Questions to take into your next leadership meeting
- Who owns the cyber risk register, and when did the board last review evidence of control effectiveness?
- Which unresolved findings could interrupt our most important business processes?
- How do we verify that external providers are meeting agreed responsibilities?
For a practical starting point, your leadership team can request a consultation.
Related reading: Business Cybersecurity: Why It’s No Longer Just an IT Issue
External guidance: NIST Cyberframework
For more information on strengthening your organization’s security posture, call 223-TECH (223-8324) or request a consultation.