
Over the last couple of weeks, we’ve been speaking about Business Process Reengineering (BPR) and Business Productivity Tools (BPT).
Today, I want to share some stories of our customer experiences and how we determine which productivity tool is the best fit for their organization.
We have found that after performing BPR with customers, there is an expectation that the next step is the installation of all our Business Productivity Tools into their environment. To the contrary, our business model focusses on matching our customers with applications that are best suited to their environmental needs, whether off-the-shelf or proprietary software. Therefore, if the best fit for your business is the implementation of one or combination of our 360 Suite Productivity Tools 1 (360HRM | 360IMS | 360RMS | 360PMS | 360DMS), then that shall be our recommendation. Conversely, it may be a hybrid where the business environment functions best with integration across multiple platforms.
THE CUSTOMER EXPECTATION
I’ll give you an example, we have a customer in the Retail Sector that was looking for an application to manage their stock flow. 360IMS – Inventory Management Solution enables organizations to track inventory levels, orders, sales and deliveries. However, some of the features that this particular customer was looking for would require further development of the program. Instead of offering that program, we contacted external vendors. We assessed other vendors offerings, because our customer needed the software to manage and monitor product expiration dates – this feature is not usually part of an inventory management solution.
OUR SOLUTION
We held consultations with a number of vendors to ensure that their products matched the scope of the job. We then facilitated Virtual meetings with the client and the vendor to ensure there was a best fit.
These are some of the things that we do. Our goal is to ensure the technology integrated aligns with our customers’ mandate. Finding the solution that will ensure that your business operates optimally is of paramount importance to us. We work together with other vendors to create the best possible outcomes for you and your business.
Stay tuned to our next blog where we talk more about 360HRM – one of productivity tools and in the meantime, schedule a consult with us to see which Productivity Tools will work best for your business.
Our Blog
Your Business Continuity Plan: Does Everyone Know Their Role?
A business continuity plan is only as strong as its people Your business continuity plan lists the production manager, sales lead and communications officer. But have those employees ever rehearsed their responsibilities? If not, the document may offer comfort...
Cyberattacks Are Getting Faster. Is Your Business Ready to Respond?
800 TECH | EXECUTIVE CYBER BRIEF 18 NOVEMBER 2026 | 2-MINUTE READ The business issue: Cybercriminals are using artificial intelligence to automate attacks against businesses, reducing the time and effort needed to identify weaknesses, exploit systems and gain...
What Should Leaders Do in the First Hours of a Cyber Incident?
The first hours should activate a cyber incident response plan A finance employee notices unusual messages from a trusted supplier. Soon afterward, colleagues report suspicious sign-in activity. Should the organization disable an account, halt payments or contact...
How Long Can Your Business Operate Without Critical Systems?
Which critical systems keep your business operating? Imagine a Caribbean manufacturer whose production scheduling system becomes unavailable during a busy delivery week. Employees may still arrive at work, yet orders, dispatch and customer commitments quickly suffer....
Who Is Accountable for Cybersecurity in Your Business?
Why cybersecurity accountability belongs in the boardroom? A supplier’s compromised account can cause your organization’s problem overnight. When a payment instruction changes or a customer cannot access a service, clients will look to the business, not its IT...
Cybersecurity Governance: Why Strong Leadership Matters More Than Red Tape
When business leaders hear the word governance, they often think of bureaucracy, lengthy approval processes, additional policies and unnecessary restrictions. However, effective cybersecurity governance should achieve the opposite. It should help organizations make...
Cybersecurity Risk Management: Don’t Just Pay for Security, Test It!
Many organizations still think about cybersecurity in much the same way they think about insurance: something they pay for in case something goes wrong. It is an understandable comparison, but it creates a dangerous mindset. Cyber insurance can help absorb part of the...
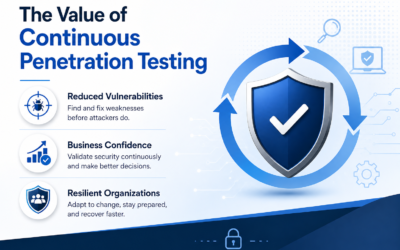
Continuous Penetration Testing: Why Modern Businesses Must Continuously Validate Security
Why Continuous Penetration Testing Matters Business environments never stand still. Every software update, cloud migration, vendor integration, employee onboarding, or configuration change introduces new opportunities for cyber attackers. Therefore, organizations can...
Business Cybersecurity: Why It’s No Longer Just an IT Issue
Business Cybersecurity Is About Business Survival For years, many organizations viewed cybersecurity as the responsibility of the IT department. However, today's business environment tells a different story. Every new employee, cloud application, software update, AI...